



NIS 2 applies. What matters now is what you can prove..
Registered. Now what? What's needed is evidence of your risk management, your reporting channels, and how sensitive data leaves your organisation.
Where implementation stands in 2026.
6 December 2025
The NIS 2 Implementation Act applies with no transition time.
6 March 2026
End of the registration deadline with the BSI.
31 July 2026
End of the grace period for late registrations.
Over 19,000
entities have registered so far, according to the BSI.
Three pieces of evidence that are usually missing. Many organisations have made progress technically. Evidence is often missing where data leaves the building.
1. Which channels does data use to leave your organisation?
A channel nobody knows about remains a gap, even if nothing has gone wrong yet. Start with a list: which channels do your staff actually use?
2. Who accessed which data, and when?
NIS 2 requires documentation, not spot checks. Once logs are generated automatically, this question is answered in minutes rather than weeks.
3. How do you vet your suppliers and service providers?
Security questionnaires sent by email are hard to keep track of. Structured forms and data rooms build the evidence trail as you go.
Which evidence could you produce today?
Work through our checklist to cover the key points and see exactly where you stand.
Control and document the way data leaves your organisation with FTAPI
FTAPI secures the point that gets messy in everyday operations: exchange with external parties. Sensitive data travels defined routes instead of workarounds. The secure route becomes the easiest one.
Every send, every retrieval and every release is logged. You export it and produce it as evidence. German hosting, certified to BSI C5 Type 2 and ISO/IEC 27001/27017/27018.
Your industry in focus. Select your sector and find out how FTAPI supports you with the specific requirements.
Maintaining operational capability
Cyber attacks threaten the state’s operational capability. Incidents such as the attack on Südwestfalen-IT in October 2023 demonstrated just how vulnerable digital administrative structures are. NIS 2 therefore demands strengthened protection of ICT systems and robust contingency plans.
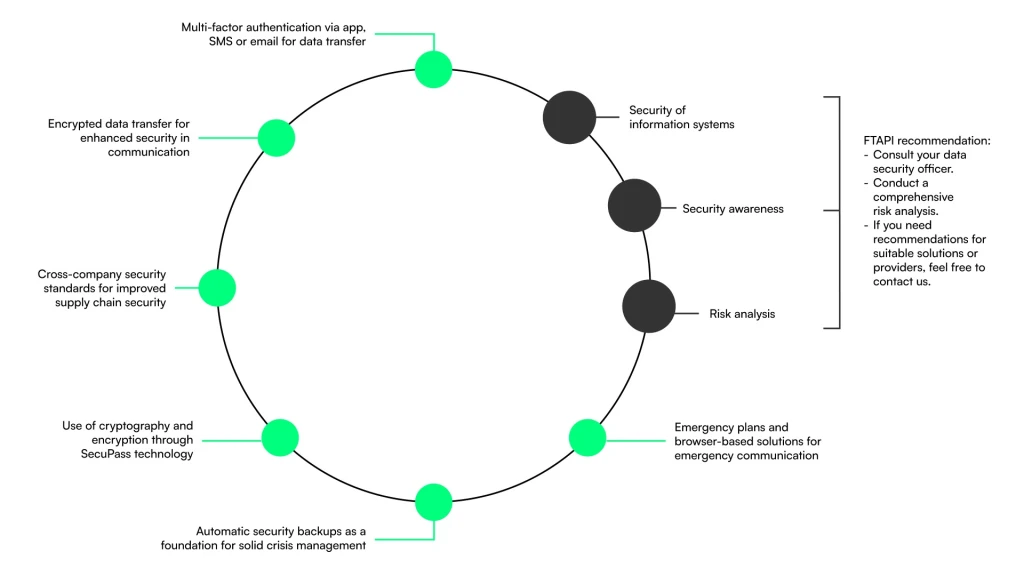
FTAPI encrypts your external data exchange end-to-end and provides an independent communication channel for crisis situations. This allows you to close security gaps in email traffic and reliably fulfil statutory documentation requirements.
Maximum protection for patient data
IT outages threaten patient care. NIS 2 therefore requires the highest level of protection for all digital processes, extending beyond organisational boundaries—for example, when medical reports or laboratory results are sent to external partners.
FTAPI seamlessly integrates GDPR-compliant data protection into your daily routine: send medical reports and laboratory results to external partners with end-to-end encryption. This prevents data leakage and effectively protects you against malware attacks.
Securing supply chains and intellectual property
NIS 2 demands stricter standards for supply chain security. Insecure emails with suppliers are often the weakest link; a cyber attack via this route can lead to production shutdowns lasting for weeks.
FTAPI protects sensitive CAD data and blueprints in virtual data rooms and hardens data transfer against industrial espionage. This keeps your production running and satisfies strict industry compliance requirements.
Efficiently meeting DORA and NIS 2 requirements
Although DORA takes precedence, NIS 2 affects you indirectly: disruptions in customer portals or insecure channels for contract data now explicitly violate statutory due diligence obligations regarding business continuity. Furthermore, the executive board is personally liable for cyber risks.
FTAPI secures your customer communication in an audit-compliant manner and automatically provides comprehensive audit trails. This allows you to provide the required compliance evidence for the BSI, BaFin, and your partners at the touch of a button, minimising liability risks.
Verified and certified security for your data.

Frequently asked questions.
The previous NIS Directive focused on operators of critical infrastructure. NIS 2 brings significantly more organisations into scope. Whether you're affected depends on two factors: your sector and your size. Affected entities have to check this themselves — there's no letter in the post to tell you.
Affected sectors include, among others:
Energy and drinking water
Transport
Financial market infrastructure
Healthcare
Digital infrastructure and digital services
Central public administration
Manufacturing and waste management
A note on public administration: the federal act doesn't explicitly name states (Länder) and local authorities. State-level legislation has been announced, though progress varies by state. Municipal utilities, local authority-owned enterprises and municipal IT providers can nonetheless be captured as entities in their own right, independently of this.
Since 6 December 2025, with no transition period. The BSI registration deadline expired on 6 March 2026, and the BSI's grace period ended on 31 July 2026.
Registration triggers the substantive obligations: risk management across the ten areas under § 30 BSIG, reporting duties (24-hour early warning, 72-hour report, one-month final report), plus oversight and training duties for management under § 38 BSIG. Operators of critical facilities must additionally provide regular evidence under § 39 BSIG.
No single measure will do it. NIS 2 requires organisation, process and technology together. It starts with a risk assessment, from which you derive your measures. FTAPI covers data exchange with external parties, including the evidence for it.
Since NIS 2 is an EU directive, the same conditions apply across the entire EU, including Austria. Switzerland, however, is not an EU member. Nevertheless, due to close economic ties between Switzerland and the EU—particularly in trade—the NIS 2 Directive is likely to have an indirect impact on Swiss organisations.
For essential entities, fines of up to €10 million or 2% of worldwide annual turnover; for important entities, up to €7 million or 1.4% — whichever is higher in each case. A separate fine applies specifically for failing to register.
Discover more.

Blog
Implement incident response management.
Here is how to set up your emergency communications in compliance with DORA and NIS-2, ensuring you remain capable of taking action in a crisis.

Guide
Use NIS-2 as a lever for digital efficiency.
In our free guide, we'll show you in more detail how you can use NIS-2 as a strategic upgrade for your daily operations.

Blog
NIS-2 Implementation as a Lever for Digital Efficiency
Companies can use the implementation of the NIS-2 directive as an opportunity to future-proof and automate their processes.
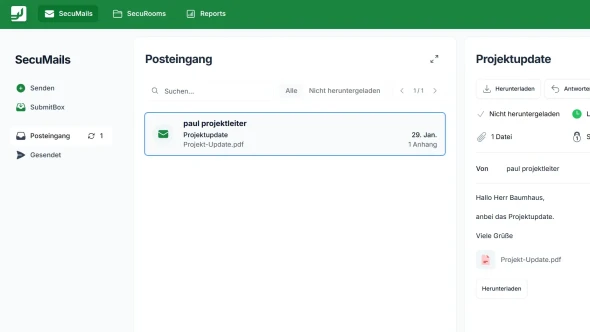
Product
SecuMails: Secure emails made easier than ever
Send encrypted emails with just one click—directly from Outlook or your browser.